ISMS Consultation & Implementation
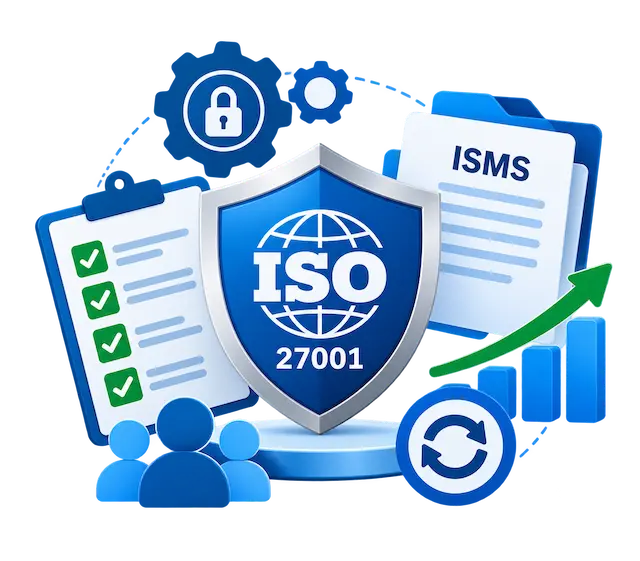
ISMS Consultation & Implementation Overview
Condition Zebra’s ISMS Consultation & Implementation service helps organisations establish a structured, practical, and sustainable Information Security Management System aligned with ISO/IEC 27001. From initial gap assessment and risk management to policy implementation, internal audit readiness, and continuous improvement, we help embed information security into your organisation’s day-to-day operations.
ASSESS
Understand Your Current Security Posture
Evaluate existing policies, processes, security controls, governance, and risk management practices against ISO/IEC 27001 requirements to identify gaps and improvement areas.
IMPLEMENT
Put Policies & Controls into Practice
Develop and implement the required policies, procedures, security controls, operational processes, and employee responsibilities needed to establish an effective ISMS.
DESIGN
Build Your ISMS Framework
Define the ISMS scope, governance structure, roles and responsibilities, risk methodology, objectives, and control framework based on your organisation’s business and security requirements.
VALIDATE
Prepare for Audit & Certification
Review ISMS effectiveness, conduct internal audit activities, identify non-conformities, support corrective actions, and strengthen readiness for ISO/IEC 27001 certification.
MANAGE
Assess & Treat Information Security Risks
Identify and evaluate information security risks, establish risk priorities, select appropriate treatments, and develop a structured Risk Treatment Plan.
IMPROVE
Maintain & Continuously Strengthen Your ISMS
Establish ongoing monitoring, management review, corrective actions, performance measurement, and continuous improvement practices to keep the ISMS effective as risks and business requirements evolve.
ISO 27001 Readiness • Stronger Governance • Risk-Based Security • Improved Resilience • Audit Readiness
• Continuous Improvement
ISMS Framework Coverage
Governance & Leadership
Roles, responsibilities, accountability, management commitment, and organisational context.
Risk Management
Risk identification, assessment, treatment, acceptance, and ongoing monitoring.
Asset & Information Protection
Asset ownership, classification, information handling, and protection requirements.
Access & Security Controls
Identity and access governance, operational controls, and appropriate security measures.
Incident & Operational Resilience
Incident management, security operations, response processes, and resilience.
Compliance & Continuous Improvement
Legal and regulatory obligations, monitoring, internal audits, management reviews, and continual improvement.
Our ISMS Implementation Approach
We follow a structured, step-by-step methodology designed for practical execution and audit readiness.
1. Gap Assessment & Discovery
We assess your current security posture against ISO 27001 requirements.
- Review existing policies and controls
- Identify compliance gaps
- Evaluate current risk management practices
2. ISMS Design & Framework Development
We design a tailored ISMS structure based on your organisation’s size, industry, and risk profile.
- Define ISMS scope
- Establish governance model
- Develop risk assessment methodology
- Design control framework
3. Policy & Control Implementation
We implement required policies and security controls.
- Information security policies
- Access control procedures
- Incident response framework
- Data protection and classification controls
4. Risk Assessment & Treatment Plan
We help you formalise your risk management approach.
- Risk identification and analysis
- Risk scoring and prioritisation
- Risk treatment plan development
- Residual risk acceptance framework
5. Awareness & Training
We ensure your employees understand their security responsibilities.
- ISMS awareness sessions
- Role-based security training
- Policy adoption guidance
6. Internal Audit & Certification Readiness
We prepare your organisation for ISO 27001 certification.
- Internal audit simulation
- Non-conformance identification
- Corrective action planning
- Certification body readiness support
Key Benefits
-
ISO 27001 Certification Readiness
Structured pathway towards achieving international security certification. -
Strong Security Governance
Clear roles, responsibilities, and accountability across the organisation. -
Risk-Based Security Approach
Security decisions driven by risk analysis, not assumptions. -
Improved Operational Resilience
Better preparedness against cyber incidents and disruptions. -
Regulatory Confidence
Supports compliance with industry regulations and customer requirements.
Frequently Asked Questions (FAQs)
1. What is an Information Security Management System (ISMS) ?
An ISMS is a structured framework of policies, processes, responsibilities, and security controls used to systematically manage an organisation’s information security risks. It helps ensure information security is managed, measured, monitored, and continuously improved across the organisation.
2. How does ISMS implementation support ISO/IEC 27001 certification ?
An ISMS forms the foundation for ISO/IEC 27001 certification. Condition Zebra helps your organisation assess existing gaps, establish the required ISMS framework, conduct risk assessments, implement policies and controls, and prepare for internal audits and certification readiness.
3. What does the ISMS Consultation & Implementation service cover ?
The service covers the complete ISMS implementation journey, including gap assessment, ISMS scope and framework design, risk assessment and treatment, policy and control implementation, security awareness, internal audit preparation, corrective actions, and continuous improvement.
4. How long does it take to implement an ISMS ?
The implementation timeline depends on factors such as your organisation’s size, ISMS scope, existing security maturity, complexity of operations, available resources, and current compliance gaps. Following the initial assessment, we can establish a structured implementation roadmap based on your organisation’s requirements.
5. Do you only provide ISMS documentation ?
No. Our approach focuses on practical implementation, not documentation alone. We help organisations establish policies, processes, responsibilities, risk management practices, and security controls that can be incorporated into daily operations and maintained over time.
6. What will we receive after the ISMS implementation engagement ?
Deliverables may include an ISMS Scope Definition Document, ISO/IEC 27001-aligned ISMS Framework, Risk Assessment & Treatment Plan, Security Policies & Procedures, Internal Audit Checklist, and Certification Readiness Report, providing a structured foundation for ongoing ISMS management and certification preparation.
Why Choose Condition Zebra
Condition Zebra combines cybersecurity expertise, practical implementation experience, and a structured approach to help organisations establish an ISO/IEC 27001-aligned ISMS that works in practice—not just on paper. We focus on building a sustainable security management framework that supports your business, compliance, and risk management objectives.
ISO 27001-Aligned Expertise
Build your ISMS around ISO/IEC 27001 requirements and recognised information security practices, helping identify compliance gaps, establish appropriate controls, and strengthen your organisation’s certification readiness.
Practical Implementation Approach
Go beyond documentation with hands-on guidance to develop policies, implement controls, establish risk management processes, define responsibilities, and integrate ISMS requirements into day-to-day business operations.
Risk-Based & Business-Aligned
Develop an ISMS based on your organisation’s actual information security risks, business objectives, operational environment, and compliance requirements, ensuring security investments are focused where they matter most.
End-to-End ISMS Support
Receive structured support throughout the ISMS journey—from gap assessment and framework design to risk treatment, policy implementation, internal audit preparation, corrective actions, and continuous improvement.