Cyber Security Scorecard
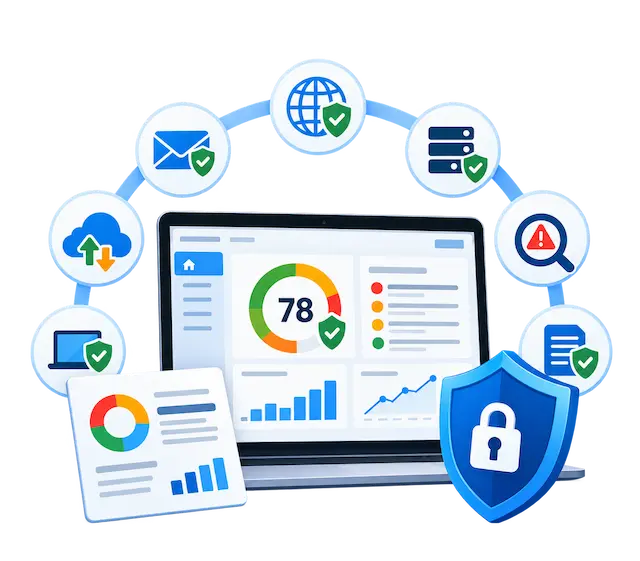
Cyber Security Scorecard Overview
A Cyber Security Scorecard is a comprehensive evaluation of your organization’s security posture across multiple domains, presented in a clear, easy-to-understand scoring format.
It helps answer critical questions:
- How secure is your organization today?
- Where are your biggest risks?
- How do you compare to industry standards?
- What should you fix first?
COLLECT
Gather Security Data
Collect relevant internal and external security data across your infrastructure, systems, domains, endpoints, vulnerabilities, and threat exposure.
SCORE
Measure Your Security Health
Translate assessment findings into clear, risk-based scores and ratings that provide an easy-to-understand view of your organisation’s current cybersecurity posture.
ASSESS
Evaluate Security Posture
Assess key security areas including external exposure, network security, email and domain protection, vulnerability management, endpoint hygiene, and threat intelligence.
PRIORITISE
Focus on Critical Risks
Prioritise identified weaknesses based on risk level, exposure, and potential impact so your organisation can focus resources on the areas that matter most.
ANALYSE
Identify Risks & Weaknesses
Correlate findings across multiple security domains to uncover vulnerabilities, configuration weaknesses, exposed assets, leaked credentials, and other security risks.
IMPROVE
Strengthen Your Security Posture
Receive actionable recommendations and a remediation roadmap to address security gaps, improve your score, and track cybersecurity improvements over time.
External Attack Surface • Network & Infrastructure • Email & Domain Security • Patch & Vulnerability Management • Endpoint & System Hygiene • Threat Intelligence & Reputation
Measure Security Posture • Identify Key Risks • Benchmark Performance • Prioritise Remediation • Track Improvement
What We Evaluate
We evaluate your cybersecurity posture across six key areas to identify security gaps, measure risk exposure, and provide a clear view of where improvements are needed.
External Attack Surface
- Exposed IP addresses, domains, and services
- Open ports and misconfigured systems
- Shadow IT and unknown assets
-
Network & Infrastructure Security
- Firewall and network security configurations
- Network segmentation and access controls
- Vulnerability exposure
Email & Domain Security
- SPF, DKIM, and DMARC configurations
- Phishing and email spoofing risks
- Domain security and reputation
-
Patch & Vulnerability Management
- Missing patches and outdated systems
- Known vulnerabilities (CVEs)
- Remediation status and timelines
Endpoint & System Hygiene
- Endpoint protection status
- System configuration weaknesses
- Unauthorised software and access
-
Threat Intelligence & Reputation
- Dark web exposure
- Leaked or compromised credentials
- Blacklist and reputation issues
Our Methodology
Data Collection
Gather internal and external security data
Analysis
Correlate findings across multiple domains
Scoring
Assign risk-based scores and ratings
Reporting
Present results in a clear scorecard format
Recommendations
Provide prioritized remediation actions
Key Benefits
- Clear Visibility
Understand your cybersecurity posture at a glance - Prioritized Actions
Focus on what matters most based on risk - Executive Reporting
Translate technical risks into business insights - Continuous Monitoring
Track improvements over time - Benchmarking
Compare your security posture against industry standards
Frequently Asked Questions (FAQs)
1. What is a Cyber Security Scorecard ?
A Cyber Security Scorecard provides a measurable view of your organisation’s cybersecurity posture by assessing key security areas and translating findings into clear scores, risk ratings, and actionable insights.
2. What areas are evaluated in the Cyber Security Scorecard ?
The assessment covers key areas including external attack surface, network and infrastructure security, email and domain security, patch and vulnerability management, endpoint and system hygiene, and threat intelligence and reputation.
3. How is the Cyber Security Score calculated ?
Security findings are analysed and evaluated based on factors such as risk severity, exposure, configuration weaknesses, vulnerabilities, and security controls. The results are translated into scores and risk levels to provide an easy-to-understand view of your security posture.
4. What can the Cyber Security Scorecard help us identify ?
The scorecard can highlight risks such as exposed assets, open ports, insecure configurations, missing patches, known vulnerabilities, email security weaknesses, leaked credentials, and reputation issues, helping you understand where improvements are needed.
5. What will we receive after the assessment ?
You will receive a Cyber Security Scorecard, detailed risk breakdown, executive summary, risk prioritisation, and remediation recommendations to help your organisation address identified weaknesses and improve its security posture.
6. How often should a Cyber Security Scorecard assessment be performed ?
Cybersecurity posture changes as systems, vulnerabilities, threats, and configurations evolve. Assessments should be performed periodically and after significant infrastructure or security changes to track improvements, identify new risks, and maintain visibility over your security posture.
Why Choose Condition Zebra
Local cybersecurity expertise backed by experienced security professionals, data-driven assessment, comprehensive security visibility, and practical recommendations to help organisations measure their cybersecurity posture, understand key risks, and prioritise meaningful security improvements.
Data-Driven Insights
Gain an objective view of your cybersecurity posture through measurable security metrics, risk-based scoring, and evidence-based findings across key security areas.
Holistic Coverage
Assess security from both internal and external perspectives, covering your attack surface, infrastructure, email and domains, vulnerabilities, endpoints, and threat exposure.
Business-Focused Reporting
Translate complex cybersecurity findings into clear scores, risk ratings, and business-relevant insights that help management understand security priorities and make informed decisions.
Actionable Recommendations
Receive clear, prioritised remediation recommendations that help your organisation address critical weaknesses, improve its security score, and strengthen its overall cybersecurity posture.