Cybersecurity Maturity Assessment
Cybersecurity Maturity Assessment Overview
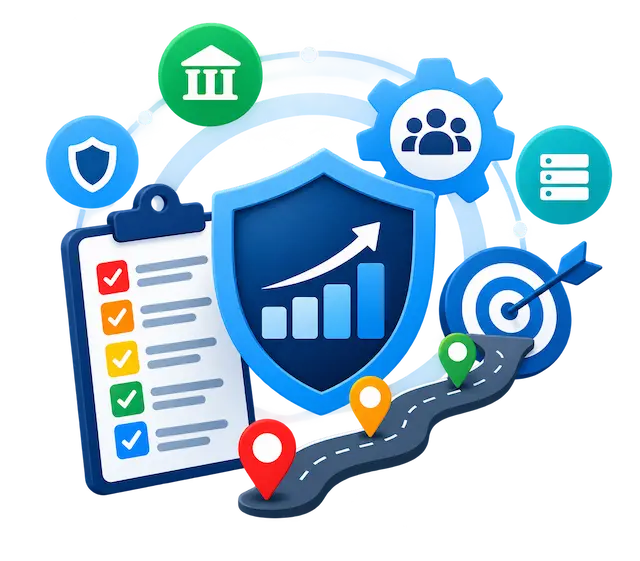
Condition Zebra’s Cybersecurity Maturity Assessment provides an objective view of how effectively your organisation manages cybersecurity across people, processes, and technology. We assess your current capabilities against recognised cybersecurity frameworks, identify maturity gaps, and develop a risk-based improvement roadmap to help you progress from reactive security towards a more proactive and measurable cybersecurity programme.
DISCOVER
Understand Your Security Environment
Gather information through stakeholder interviews, documentation reviews, and analysis of your technology environment to understand existing cybersecurity practices and capabilities.
SCORE
Measure Your Current Maturity Level
Score each cybersecurity domain using a structured five-level maturity model, from Initial and Developing through to Defined, Managed, and Optimised.
ASSESS
Evaluate Your Cybersecurity Capabilities
Assess security controls, governance, processes, technologies, and organisational practices across key cybersecurity domains to determine how effectively they are implemented and managed.
PRIORITISE
Identify Gaps & Focus on What Matters
Compare current and target maturity levels to identify critical gaps and prioritise improvements based on cyber risk, business impact, and security objectives.
BENCHMARK
Compare Against Recognised Frameworks
Map your cybersecurity capabilities against recognised frameworks such as NIST Cybersecurity Framework, ISO/IEC 27001 controls, and CIS Critical Security Controls to establish an objective maturity baseline.
IMPROVE
Build Your Cybersecurity Roadmap
Develop a clear, risk-based improvement roadmap with practical recommendations to strengthen capabilities, guide security investments, and continuously improve cybersecurity maturity.
Clear Security Visibility • Measurable Maturity • Prioritised Improvements
• Smarter Security Investment
• Board-Level Insights • Strategic Roadmap
Cybersecurity Maturity Coverage
Governance & Risk
Security leadership, policies, responsibilities, risk management, and cybersecurity governance.
Assets & Data Protection
Asset visibility, classification, encryption, backup, data handling, and protection controls.
Identity & Access Security
User access, authentication, MFA, privileged access, and identity governance.
Infrastructure & Endpoint Security
Network architecture, segmentation, firewalls, endpoints, servers, and device protection.
Detection, Response & Recovery
Security monitoring, logging, threat detection, incident response, recovery, and resilience.
People & Third-Party Risk
Security awareness, phishing resilience, employee responsibilities, vendor risk, and supply chain security.
Assessment Methodology
We follow a structured and evidence-based approach:
1. Information Gathering
- Stakeholder interviews (IT, Security, Management)
- Policy and documentation review
- System architecture analysis
2. Technical Evaluation
- Security control validation
- Configuration review (where applicable)
- Tool and technology assessment
3. Framework Mapping
We map your controls against:
- NIST CSF
- ISO 27001 Annex A controls
- CIS Controls
4. Maturity Scoring
Each domain is scored to determine:
- Current maturity level
- Target maturity level
- Gap severity
5. Reporting & Recommendations
We provide a clear roadmap for improvement.
Key Benefits
-
Clear Security Visibility
Understand exactly where your organisation stands today. -
Prioritised Investment Strategy
Focus resources on the most critical security gaps. -
Improved Risk Management
Identify and reduce high-impact cybersecurity risks. -
Board-Level Reporting
Translate technical security posture into business risk language. -
Strategic Security Roadmap
Move from reactive security to structured, long-term maturity growth.
Frequently Asked Questions (FAQs)
1. What is a Cybersecurity Maturity Assessment ?
A Cybersecurity Maturity Assessment evaluates how effectively your organisation’s cybersecurity capabilities are designed, implemented, and managed across people, processes, and technology. It provides a measurable view of your current security maturity and identifies areas that require improvement.
2. What areas are covered in the assessment ?
The assessment covers key cybersecurity domains including Governance & Risk, Asset Management, Identity & Access Management, Network Security, Endpoint Security, Security Monitoring, Incident Response, Data Protection, Security Awareness, and Third-Party Risk.
3. What cybersecurity frameworks are used for benchmarking ?
Your cybersecurity capabilities can be benchmarked against recognised frameworks and standards such as the NIST Cybersecurity Framework (CSF), ISO/IEC 27001 controls, and CIS Critical Security Controls, providing a structured baseline for evaluating maturity.
4. How is our cybersecurity maturity level measured ?
Each security domain is evaluated using a structured five-level maturity model: Initial, Developing, Defined, Managed, and Optimised. This helps establish your current maturity level, desired target level, and the gaps that need to be addressed.
5. How is a Cybersecurity Maturity Assessment different from a security audit ?
A security audit typically focuses on whether specific requirements or controls are being met. A Cybersecurity Maturity Assessment looks more broadly at how well cybersecurity capabilities are established, integrated, measured, and continuously improved, helping your organisation develop a longer-term security strategy.
6. What will we receive after the assessment ?
You will receive clear, business-focused deliverables that may include a Cybersecurity Maturity Scorecard, Detailed Gap Analysis Report, Risk-Based Prioritisation Matrix, Board-Level Executive Summary, and a 12–24 Month Security Improvement Roadmap to guide future cybersecurity improvements.
Why Choose Condition Zebra
Condition Zebra combines cybersecurity expertise, recognised security frameworks, and a practical, risk-based approach to help organisations understand their true cybersecurity maturity—not simply whether security controls exist. We translate assessment findings into measurable insights and prioritised actions that support better security decisions, investments, and long-term improvement.
Framework-Based Assessment
Benchmark your cybersecurity capabilities against recognised frameworks such as NIST Cybersecurity Framework, ISO/IEC 27001 controls, and CIS Critical Security Controls, providing a structured and objective view of your security maturity.
Holistic Security Evaluation
Assess cybersecurity across people, processes, and technology, covering critical areas such as governance, risk, identity, infrastructure, data protection, security monitoring, incident response, awareness, and third-party risk.
Risk-Based Prioritisation
Focus improvement efforts where they matter most by identifying maturity gaps and prioritising them according to cybersecurity risk, business impact, current capabilities, and organisational objectives.
Actionable Improvement Roadmap
Turn assessment findings into a clear, prioritised cybersecurity roadmap that defines current and target maturity levels, guides security investments, and supports measurable improvement over the next 12–24 months.